CriticalSecurity & Privacy
PHP2Shell: No login, no app code, no warning. What next?
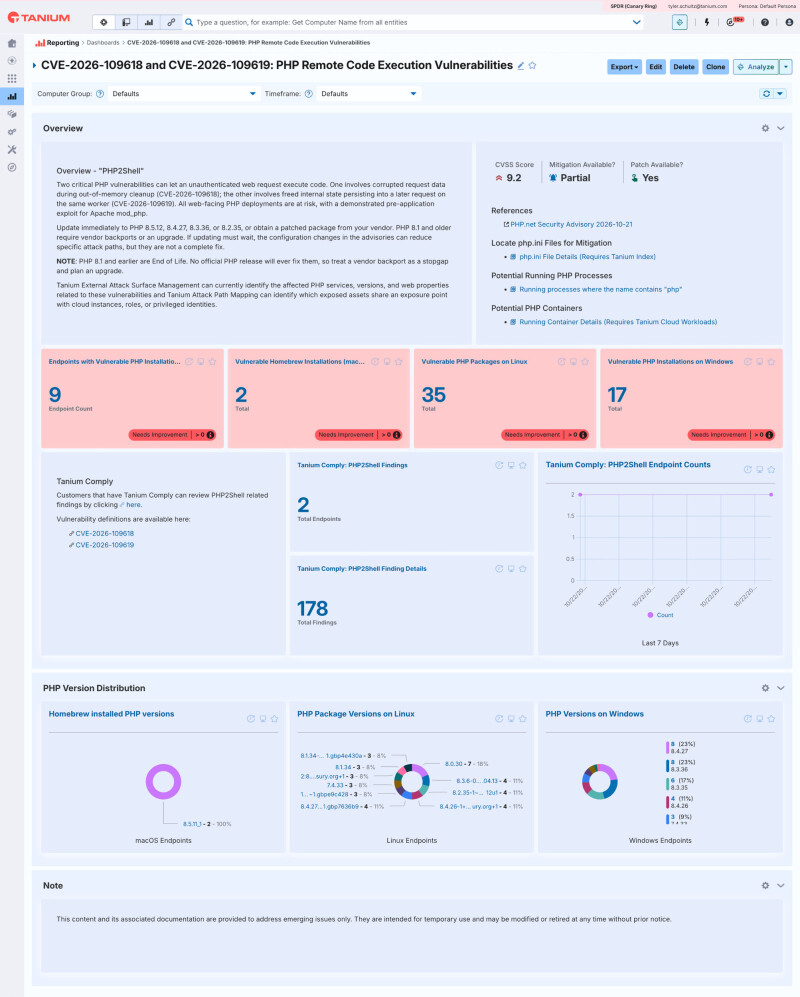
The PHP2Shell vulnerabilities in PHP core enable unauthenticated remote code execution through a crafted web request, creating immediate risk for internet-facing applications and any environment running older PHP releases. For CIOs and technology leaders, the business implication is that patching is necessary but not sufficient: the larger challenge is rapid, enterprise-wide discovery of hidden PHP instances across servers, workstations, containers, and vendor-bundled stacks so IT can prioritize exposure before exploitation matures. IT organizations should also assume active probing is underway and use log hunting plus vulnerability intelligence to focus on the most exposed assets, especially mod_php and ARM64 systems.