CriticalSecurity & Privacy
ScreenConnect Client (Ab)used by Attackers, (Thu, Oct 1st)
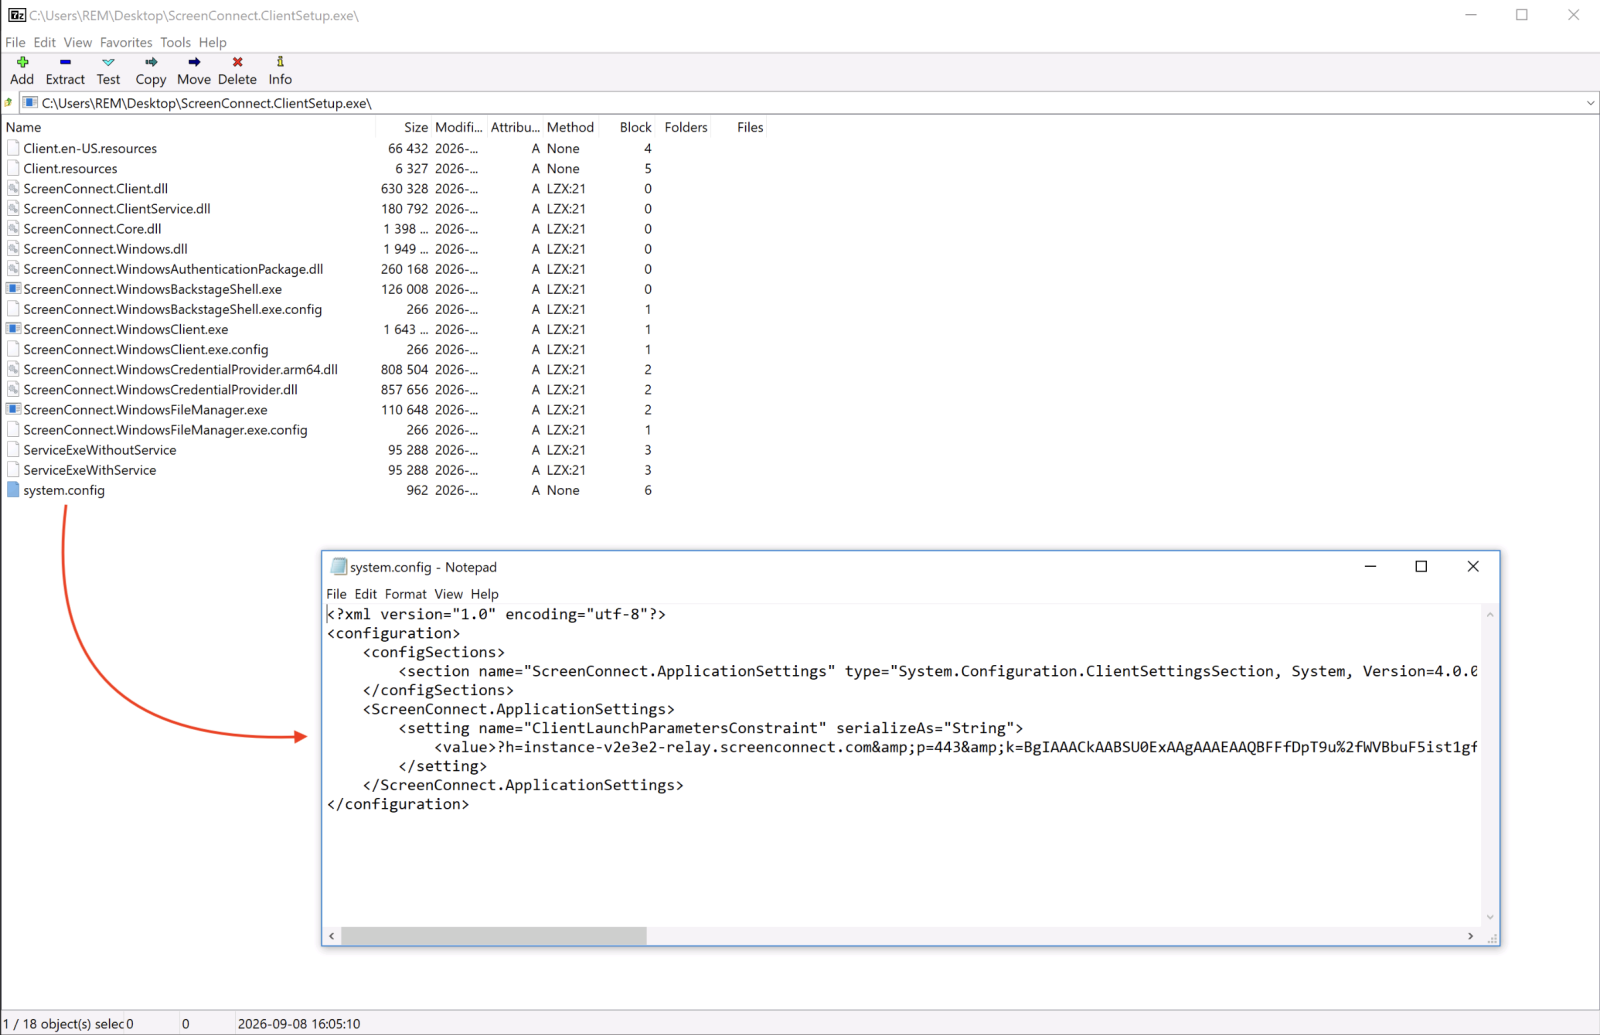
Attackers are using a signed, legitimate ScreenConnect client delivered through phishing to establish remote access, illustrating how trusted remote management tools can bypass traditional security controls and appear benign to browsers and endpoint defenses. For CIOs, this raises the strategic risk that commodity, vendor-signed software can become an attacker-controlled access path, increasing the need for stronger application control, email/web filtering, and behavioral detection rather than relying only on signature-based defenses.
SANS Internet Storm Center2 min read