ImportantSecurity & Privacy
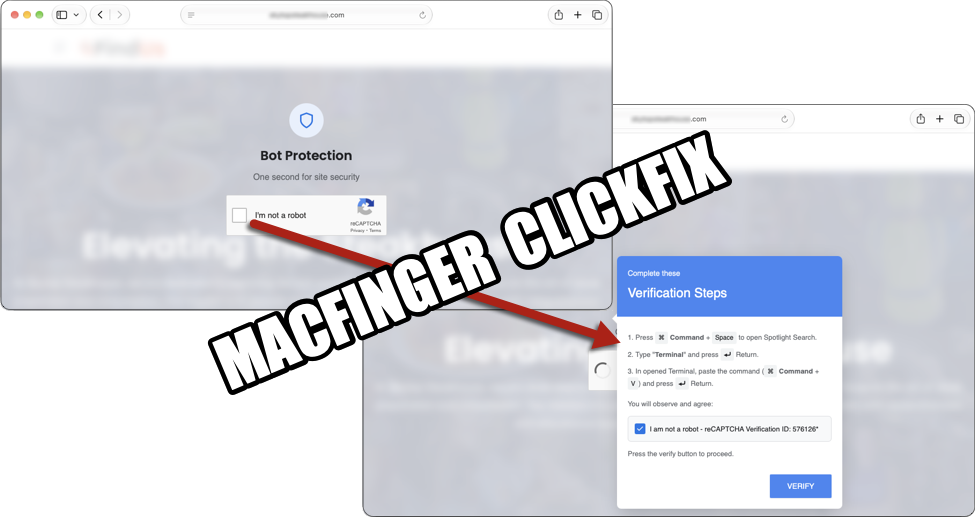
A Closer Look at Malware From the Macfinger ClickFix Campaign, (Fri, Sep 25th)
The Macfinger ClickFix campaign is actively delivering a macOS information stealer that appears distinct from Atomic Stealer, using architecture-specific payloads, persistence under a masqueraded system path, and multiple exfiltration methods to capture credentials and user data. For CIOs and IT leaders, the key business risk is theft of corporate secrets, cloud and app credentials, and sensitive files from Mac endpoints, underscoring the need for stronger macOS endpoint detection, tighter privilege controls, and monitoring for suspicious Terminal/bash and permission prompts. This campaign also highlights how social engineering can bypass traditional defenses, so IT organizations should treat macOS as a high-value target alongside Windows.
SANS Internet Storm Center2 min read