Authorization terminology is a mess: Let's fix it
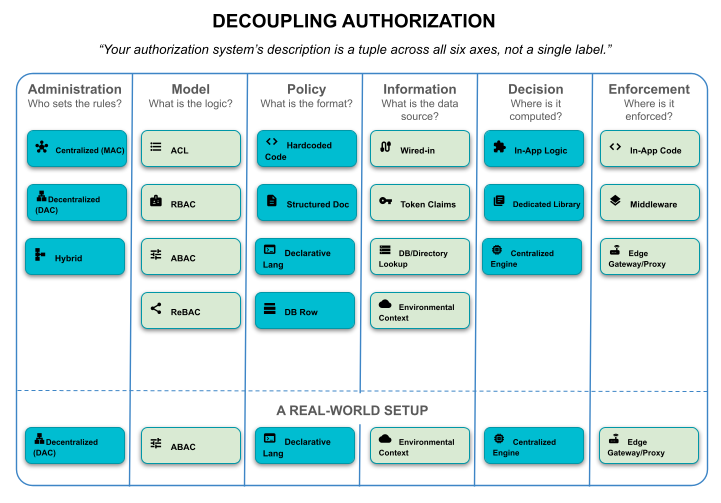
The article argues that authorization language has become strategically confusing because terms like RBAC, ABAC, PBAC, MAC, DAC, ACL, and ReBAC often describe different layers of the authorization stack rather than true competing models. For CIOs and technology leaders, the business impact is that unclear terminology can lead to poor platform decisions, misaligned security investments, and harder-to-govern access control architectures across applications, APIs, and cloud services. The key implication for IT organizations is to evaluate authorization by breaking it into separate dimensions—policy ownership, data inputs, decision logic, and enforcement—so teams can standardize architecture, reduce complexity, and improve security governance at scale.